

Introduction
Artificial intelligence and machine learning are now central to modern payment-fraud detection because the number of digital transactions is too large, too fast, and too complex for human reviewers or simple rules to analyze alone.
A traditional fraud rule might say that a transaction above a certain amount or from an unfamiliar location deserves additional scrutiny. Machine-learning systems can evaluate hundreds of signals together, compare them with historical behavior, and estimate risk in milliseconds.
Visa describes modern AI-driven fraud systems as monitoring transactions in real time and evaluating spending behavior, device information, geography, frequency, velocity, merchant context, and network-level patterns. Mastercard similarly uses AI-powered decisioning to identify suspicious behavior while helping issuers avoid unnecessary declines of legitimate customers.
The goal is not to let an algorithm make every decision blindly. Strong fraud programs combine AI models, deterministic rules, authentication, network intelligence, human review, chargeback feedback, and governance.
This article explains those concepts defensively. It does not publish fraud-score thresholds, model weights, feature cutoffs, approval conditions, or other details that could help attackers tune transactions to evade detection.
Quick Answer: How Does AI Detect Payment Fraud?
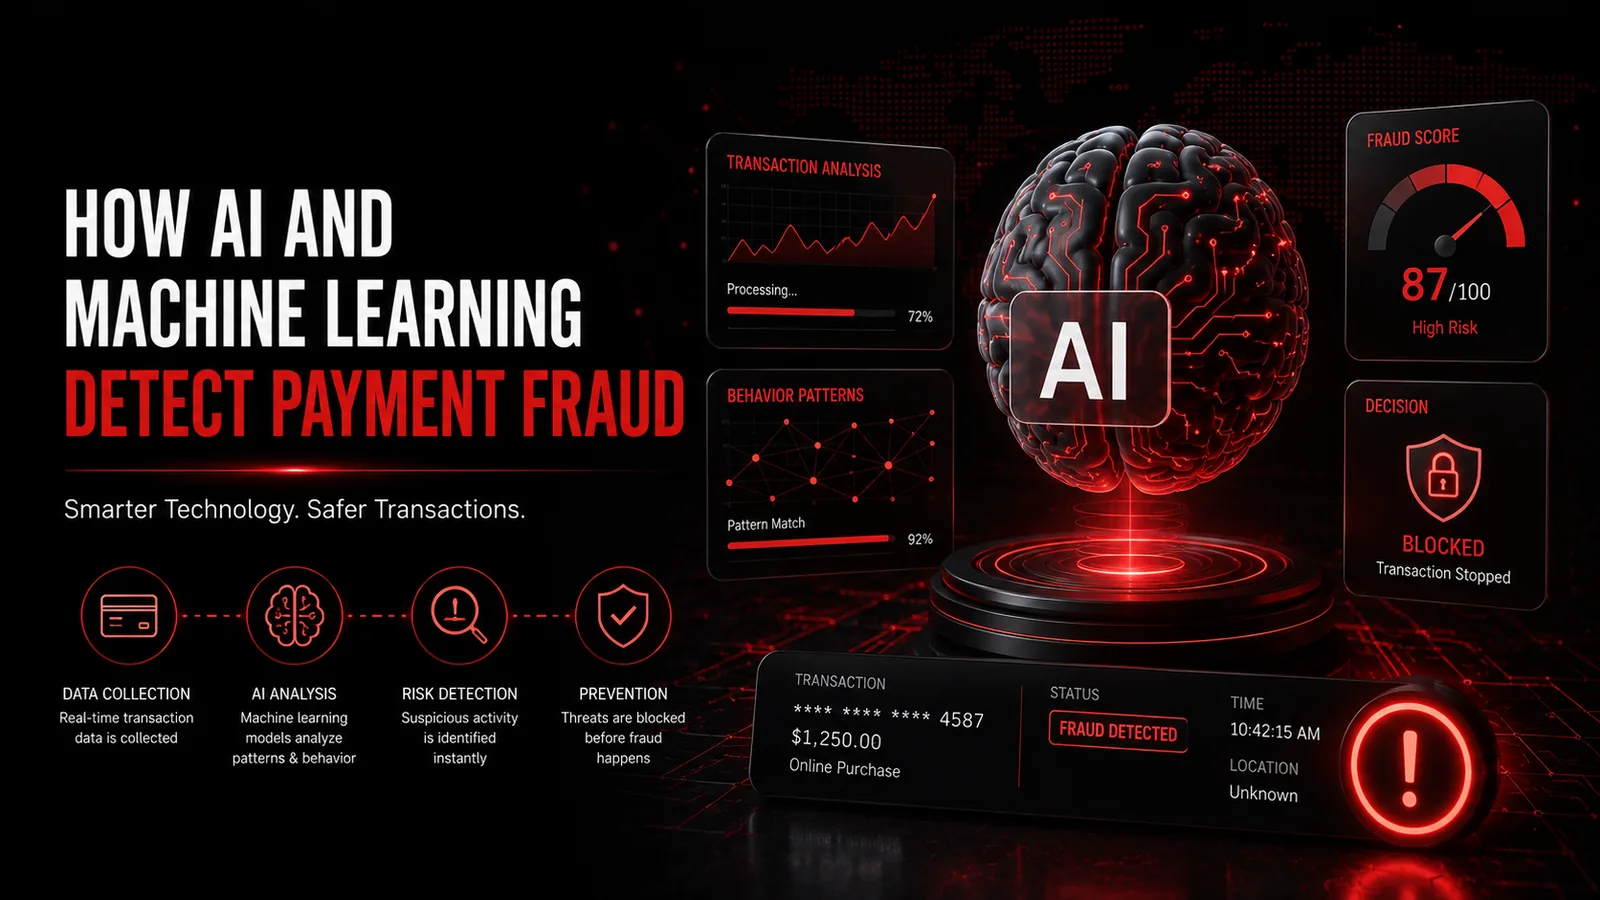
AI fraud systems compare a new transaction with patterns learned from large volumes of legitimate and fraudulent activity.
They evaluate signals such as amount, frequency, account history, merchant type, device context, location, authentication outcomes, previous disputes, and whether the behavior is normal for the customer.
The system then produces a risk assessment or score.
Low-risk activity may be approved with little friction. Medium-risk activity may receive additional authentication or manual review. High-confidence fraud may be declined, blocked, or investigated.
The model improves when confirmed outcomes such as fraud reports and chargebacks are fed back into future training and monitoring.
AI vs Machine Learning: What Is the Difference?
Artificial intelligence is a broad term for computer systems that perform tasks associated with reasoning, prediction, recognition, or decision support.
Machine learning is a major subset of AI in which models learn statistical patterns from data instead of relying only on manually written rules.
In payment fraud, the terms are often used together because production systems combine machine-learning models with rules, identity signals, network intelligence, and human decisions.
Not every fraud decision labeled 'AI' uses the same model architecture, and not every useful fraud control needs AI.
Why Payment Fraud Is a Good Use Case for Machine Learning
Payments create large volumes of structured, time-sensitive data.
Fraud is also a pattern-recognition problem: a transaction may be suspicious because of how it differs from normal activity or how it resembles known fraud.
Machine learning can identify relationships among many variables that would be difficult to express as a long list of manual rules.
The technology is especially useful when decisions must be made in milliseconds and when criminal behavior changes continuously.
Fraud Detection Is a Probability Problem
Most fraud systems do not know with certainty whether a transaction is criminal at authorization time.
They estimate probability or risk.
A transaction that appears unusual may still be legitimate. A transaction that looks ordinary may still be fraudulent.
This is why modern systems rank risk rather than treating every single signal as proof.
The business decision then balances fraud risk, customer friction, financial exposure, and available authentication options.
Signal 1: Historical Spending Behavior
One of the strongest signals is whether the transaction resembles the cardholder's or account holder's normal behavior.
A model can learn typical purchase amounts, merchant categories, time-of-day patterns, geographic patterns, and frequency.
The purpose is not to punish customers for doing something new.
Instead, unusual behavior receives additional context.
Visa's current fraud guidance explicitly describes historical spending behavior as one of the real-time signals used in AI fraud models.
Signal 2: Transaction Amount
Amount matters because a transaction can be unusual relative to the customer's history or the merchant's normal business.
A large purchase is not automatically fraudulent and a small purchase is not automatically safe.
Machine learning can evaluate amount together with customer tenure, merchant type, device context, previous purchases, and other signals.
This reduces dependence on simplistic universal limits.
Signal 3: Frequency and Velocity
Velocity describes how quickly related events occur.
A system may evaluate the frequency of transactions, authentication attempts, account changes, or payment activity over time.
The exact thresholds should remain confidential and adapt to the institution's customer base.
Visa identifies transaction frequency and velocity as examples of real-time fraud-model inputs.
Machine learning helps identify unusual combinations rather than relying only on one fixed retry count.
Signal 4: Merchant Context
The merchant itself provides context.
Models can consider merchant category, historical fraud levels, typical purchase sizes, geography, channel, and prior customer interaction.
A transaction should not be deemed fraudulent merely because it occurs at a new merchant.
Merchant context becomes useful when combined with account, device, authentication, and network signals.
Signal 5: Device Characteristics
Device context can help determine whether a transaction comes from a familiar or unusual environment.
Models may consider whether the device has been seen before, whether several accounts are associated with the same environment, or whether behavior differs significantly from previous legitimate sessions.

Devices change, browsers are upgraded, cookies are cleared, and customers buy new phones, so a new device is not proof of fraud.
Visa and Mastercard both describe device information as part of modern transaction-risk analysis.
Signal 6: Geographic and Network Patterns
Location and network context can reveal anomalies, but they must be interpreted carefully.
People travel, use mobile networks, work remotely, and route traffic through corporate infrastructure.
Machine-learning systems can evaluate geography relative to account history and other contextual information.
Visa describes geographic and network patterns as part of real-time fraud evaluation.
The model should avoid simplistic assumptions that a country, city, or network automatically equals fraud.
Signal 7: Account History
A long-standing account with consistent legitimate activity provides more context than a brand-new account.
However, established accounts can be taken over.
Models therefore consider account age together with password resets, contact-information changes, device changes, unusual purchases, and other events.
Account history is evidence, not a guarantee.
Signal 8: Authentication Outcomes
Authentication systems such as EMV 3-D Secure can provide issuer-side risk information and, where needed, additional cardholder verification.
AI models can use authentication outcomes as one part of the overall decision.
A successful authentication does not necessarily mean every transaction is safe, because social engineering and account takeover can still occur.
Likewise, a failed or abandoned challenge does not automatically prove fraud.
Signal 9: Behavioral Patterns
Behavioral analysis looks at how an account or customer interacts with a service.
Visa describes behavioral risk management using AI as a way to identify anomalies before fraud occurs.
Examples can include changes from established account activity, unusual interaction sequences, or patterns associated with automation.
Behavioral signals should be privacy-conscious and tested carefully for false positives and bias.
Signal 10: Network-Level Intelligence
Large payment networks can see patterns across many issuers, merchants, geographies, and transaction types that one individual merchant cannot.
This broader perspective can help identify coordinated attacks, emerging fraud trends, and relationships that are invisible in one company's local data.
Visa says its risk-scoring systems use global transaction data and fraud intelligence to support authorization decisions.
Network intelligence is one reason shared payment ecosystems can detect patterns faster than isolated rule engines.
Supervised Learning
Supervised learning trains a model using examples that have known outcomes.
In payment fraud, historical transactions can be labeled as legitimate, confirmed fraud, chargeback-related fraud, or another outcome.
The model learns which combinations of features are statistically associated with those labels.
The quality of the labels is critical.
If merchant errors or friendly-fraud disputes are incorrectly labeled as stolen-card fraud, the model can learn the wrong relationships.
Unsupervised Learning
Unsupervised methods look for unusual structures or clusters without requiring every example to have a confirmed fraud label.
This can be useful for identifying previously unseen behavior.
Anomaly detection can surface transactions that differ sharply from normal patterns.
An anomaly is not automatically fraud.
Human analysts or other models may need to determine whether the behavior represents a new legitimate pattern or an emerging attack.
Semi-Supervised and Hybrid Approaches
Real fraud systems often combine supervised and unsupervised techniques.
Confirmed fraud labels provide strong training examples, while anomaly detection can surface new behavior that the historical labels do not yet represent.
Rules can add institutional knowledge and regulatory controls.
Human analysts can investigate ambiguous cases and create better labels.

The result is a hybrid system rather than one universal algorithm.
Deep Learning
Deep learning uses multi-layer neural networks to learn complex relationships from large datasets.
Visa has publicly described deep-learning models used for real-time fraud risk scoring in payment services.
Deep learning can capture interactions among many features, but increased complexity also raises governance, explainability, monitoring, and operational requirements.
More complex is not automatically better; the model must improve real-world outcomes.
Graph and Relationship Analysis
Fraud often involves relationships rather than isolated transactions.
A graph-style representation can connect accounts, cards, devices, merchants, addresses, or other entities and identify unusual clusters.
This can help reveal coordinated activity that looks harmless when each transaction is viewed separately.
Graph analytics should be implemented with appropriate privacy, access, and governance controls.
Real-Time Risk Scoring
A common production pattern is to generate a risk score while the payment is still being authorized.
The score summarizes the model's estimate of risk using current transaction context and historical patterns.
Visa describes real-time risk scoring as a way to support authorization decisions, and Mastercard describes AI-powered decision intelligence for preventing fraud while approving genuine transactions.
The exact numeric score and decision boundary are internal controls and should not be published.
What Happens After a Risk Score Is Generated?
A risk score usually feeds a decisioning system rather than acting alone.
Depending on risk and business rules, the transaction may be approved, declined, authenticated, reviewed, delayed, or allowed with monitoring.
Different merchants and issuers can make different decisions from the same general risk level because financial exposure and customer experience differ.
The model supports the decision; it does not replace the entire fraud strategy.
Why Exact Thresholds Should Stay Private
Fraud systems lose value when attackers know exactly which score, transaction amount, retry count, or behavior triggers a block.
Criminals can alter their behavior to remain just below fixed public boundaries.
Defensive education should explain categories of signals and governance without revealing operational cutoffs.
Institutions should also change and test controls over time rather than treating thresholds as permanent.
AI vs Traditional Rules
Rules are still useful.
They are easy to understand, can implement policy quickly, and are valuable for known patterns or regulatory requirements.
But large rule sets can become brittle and difficult to maintain.
Machine learning is better suited to evaluating complex combinations and adapting to changing patterns.
Strong fraud programs commonly use both.
Why Static Rules Alone Struggle
Fraudsters adapt.
If a criminal learns that one obvious behavior is blocked, the behavior changes.
Static rules also generate false positives when legitimate customers cross arbitrary thresholds.
Machine learning can evaluate context and relationships that make a transaction risky rather than relying only on one cutoff.
Rules remain important but work best when combined with adaptive models.
False Positives: The Other Side of Fraud Detection
A false positive occurs when a legitimate transaction is incorrectly treated as fraud.
False declines cost merchants revenue and can frustrate customers.
Mastercard's 2026 fraud-prevention guidance emphasizes using AI to reduce false positives and improve authorization decisions.
Visa likewise positions AI fraud tools as balancing fraud reduction with seamless legitimate payments.
Fraud detection quality therefore includes both catching fraud and protecting good customers.
Precision, Recall, and Business Outcomes
Model evaluation involves more than overall accuracy.
Fraud is often rare compared with legitimate payments, so a model can appear highly accurate while still missing significant fraud.
Teams may evaluate measures such as precision, recall, false-positive rate, fraud loss prevented, approval rate, manual-review workload, and customer friction.
No one metric should dominate every use case.

Business impact and risk appetite matter.
Why Training Data Quality Matters
Machine learning learns from the data and labels it receives.
Incomplete, delayed, biased, or incorrect labels can produce weak models.
Chargebacks can arrive weeks after a transaction.
Customer reports can be incomplete.
Some disputes are merchant or service problems rather than stolen-card fraud.
Fraud teams therefore need disciplined data pipelines and label governance.
Feedback Loops
Confirmed outcomes should feed back into future detection.
When a transaction is confirmed as fraud, the model and related systems gain another example.
When an apparently suspicious transaction is confirmed legitimate, that also provides useful information.
Feedback loops help models adapt as behavior changes.
Poor feedback can also reinforce mistakes, so institutions need quality control.
Concept Drift
Concept drift means the statistical relationship between features and fraud changes over time.
Customers adopt new devices, merchants change checkout flows, new payment methods appear, and criminals develop new tactics.
A model that performed well last year may degrade without monitoring and retraining.
Fraud models therefore require continuous performance measurement rather than one-time deployment.
Model Monitoring
Production models should be monitored for fraud capture, false positives, approval performance, data-quality issues, and unexpected changes in behavior.
Teams should compare model performance across time and relevant customer segments.
Sudden performance changes can indicate a new fraud pattern, broken data feed, merchant change, or model problem.
Monitoring is part of the model, not an optional afterthought.
Human Review Still Matters
AI is strongest when it handles scale and prioritization.
Human analysts remain important for ambiguous cases, emerging patterns, investigation, label quality, and policy decisions.
A reviewer can understand context that a model may not have.
At the same time, manual review is expensive and slow.
AI can help route the most valuable or ambiguous cases to humans rather than requiring people to inspect every transaction.
AI-Assisted Case Prioritization
Machine learning can rank alerts so investigators focus first on the events most likely to matter.
This reduces alert fatigue.
A fraud operations team receiving thousands of equally weighted alerts can miss genuinely important cases.
Risk scoring allows limited human resources to concentrate on higher-impact or less certain activity.
Explainability
Fraud teams need enough explanation to understand why a model's decision changed.
Useful explanations can identify categories such as unusual account behavior, device context, transaction pattern, or authentication history without exposing the precise fraud-control recipe publicly.
Explainability supports analyst review, customer support, model debugging, compliance, and governance.
The appropriate level depends on the system and regulatory context.
AI Governance
Fraud models can affect customers by declining payments, requiring authentication, or triggering reviews.
Institutions therefore need governance around model ownership, testing, access, data use, change management, and escalation.
NIST's AI Risk Management Framework provides a general structure for managing AI risks across organizations.
Payment institutions should combine such governance principles with applicable financial, privacy, security, and consumer-protection requirements.
Bias and Fairness
A model can inherit bias from historical data or poorly chosen features.
Fraud teams should test whether controls disproportionately burden legitimate customers in particular markets or segments without a valid risk basis.
Geography, device type, language, or customer demographics should not become simplistic proxies for criminality.
Risk decisions should be grounded in behavior and transaction context.
Privacy and Data Minimization
Fraud detection benefits from data, but more data is not automatically better.
Institutions should collect and retain information that is necessary, lawful, and proportionate to the fraud-prevention purpose.
Access to sensitive data should be controlled.
Payment and identity information should be protected under relevant security and privacy requirements.
AI governance and payment security need to work together.
Adversarial Adaptation
Fraud detection is an adversarial environment because criminals actively change behavior in response to controls.
This is different from many ordinary prediction problems.
Attackers may vary transaction patterns, accounts, devices, timing, or social-engineering techniques when an old approach stops working.
Defenders therefore need adaptive models, hidden decision boundaries, network intelligence, and continuous monitoring.
This article intentionally avoids describing how to probe those boundaries.
Can Criminals Use AI Too?
Yes.
Visa and other payment-security organizations have warned that criminals are using AI to scale scams, automate attacks, improve social engineering, and increase operational efficiency.
Generative AI can make phishing content more convincing or scalable.
This raises the importance of behavioral, identity, and network-level detection rather than relying only on obvious spelling mistakes or static signatures.
AI creates an arms race, but defenders have the advantage of legitimate network data, authentication systems, and cross-transaction intelligence.
Generative AI vs Fraud-Detection AI
Generative AI systems create content such as text, images, audio, or code.
Fraud-detection models are usually predictive or decision-support systems designed to classify risk, detect anomalies, or rank transactions.
The technologies can overlap, but they serve different purposes.
A chatbot is not automatically a payment-fraud detector, and a transaction-risk model does not need to generate text.
AI for Account-Takeover Detection
Payment fraud often begins before checkout.
Machine learning can help detect unusual logins, device changes, password-reset patterns, contact-information changes, and behavior inconsistent with the established account.
This can identify an account-takeover attempt before stolen stored-payment credentials are used.
Account and transaction models should share relevant signals where privacy and architecture permit.
AI for Card-Not-Present Fraud
CNP transactions are well suited to contextual risk analysis because the physical card is absent.
Models can combine issuer authentication, device context, account history, merchant information, behavioral patterns, tokenization signals, authorization data, and network intelligence.
The objective is not to find one magic field proving identity.
It is to calculate whether the overall transaction fits legitimate behavior.
AI for Card-Present Fraud
Card-present fraud detection can also use machine learning.
The model may consider terminal context, transaction behavior, authentication method, merchant patterns, account history, and issuer intelligence.
EMV chip security reduces important counterfeit-card risks, but lost/stolen card fraud and other card-present threats still exist.
AI complements payment authentication rather than replacing it.
AI and EMV 3-D Secure
EMV 3DS and fraud models work well together.
3DS provides data-rich authentication and allows issuers to challenge higher-risk online transactions.
Machine-learning models can use available authentication context when assessing the transaction.
Risk-based systems aim to keep low-risk legitimate customers frictionless while adding assurance when needed.
The system should not challenge every transaction simply because AI exists.

AI and Tokenization
Tokenization reduces exposure of reusable card numbers, while AI evaluates whether the transaction itself appears legitimate.
A token can also provide contextual information about the payment relationship or device within supported systems.
These controls solve different problems.
Tokenization reduces credential value if exposed; AI helps determine whether the attempted use is suspicious.
Layered security is stronger than relying on either alone.
AI and AVS/CVV
Traditional verification signals such as AVS and CVV can still contribute to AI models.
A match or mismatch is not proof on its own.
Machine learning can place the result in context with account, device, authentication, merchant, and historical behavior.
This is one advantage of model-based risk assessment over simplistic pass/fail rules.
AI and Chargeback Data
Chargebacks can provide important fraud labels, but not all chargebacks are the same.
Some represent confirmed unauthorized use, while others reflect service disputes, subscription confusion, merchant error, or friendly fraud.
Fraud teams should classify outcomes accurately before using them to train models.
Poor label quality can increase false positives or cause the model to learn merchant-policy problems as if they were criminal behavior.
AI and Consortium Intelligence
Financial institutions and payment networks benefit from seeing patterns beyond one merchant or one account.
Consortium intelligence can identify devices, accounts, merchants, or transaction patterns associated with fraud across a broader ecosystem.
This information can strengthen risk assessment while requiring careful privacy and data-governance controls.
Large networks such as Visa and Mastercard emphasize the value of network-scale intelligence in fraud decisioning.
Why Small Merchants Usually Should Not Build Their Own Fraud AI
Training a reliable fraud model requires high-quality labeled data, infrastructure, security, monitoring, model governance, and enough transaction volume to learn useful patterns.
Most small merchants are better served by reputable payment processors or fraud platforms that already provide risk scoring, 3DS integration, tokenization, and network intelligence.
A simple homemade model can create dangerous false confidence.
Merchants should focus on correct integration, checkout security, account protection, and measuring outcomes.
How Larger Merchants Can Use AI Responsibly
Larger merchants with sufficient data and expertise can build custom models that supplement processor and network risk tools.
They should maintain controlled feature pipelines, training datasets, model registries, validation procedures, versioning, performance monitoring, and fallback strategies.
Models should be tested before deployment and monitored after release.
Fraud, payments, security, data science, legal, and customer-experience teams should share governance responsibilities.
Red-Team Testing for Fraud Models
Defensive teams can test whether models remain effective against changing fraud patterns using authorized internal simulation and synthetic data.
The purpose is to discover weak assumptions before criminals do.
Testing should not use real stolen credentials or attempt unauthorized transactions.
Controlled simulations can evaluate model resilience without harming cardholders or merchants.
Synthetic Data and Safe Testing
Synthetic payment records can represent legitimate and fraudulent patterns without exposing real cardholder information.
They are useful for development, demos, training, and testing.
Production model validation still requires representative real-world outcomes under appropriate privacy and security controls.
Synthetic data is especially useful for education because students can study fraud detection without handling stolen credentials.
What AI Cannot Do
AI cannot guarantee that every fraudulent payment will be stopped.
It cannot prove identity from one score.
It cannot eliminate phishing or social engineering.
It cannot fix insecure checkout code or weak account recovery.
It cannot replace PCI DSS, tokenization, authentication, access control, incident response, or human investigation.
It can improve detection and decision quality when those controls work together.
Common Myths About AI Payment Fraud Detection
Myth: AI knows with certainty whether a payment is fraudulent. Reality: models estimate risk from patterns and context.
Myth: AI replaces all fraud rules. Reality: production systems typically combine machine learning, rules, authentication, and human review.
Myth: More declined transactions means a better model. Reality: false declines can damage revenue and customer trust.
Myth: A model trained once will remain effective forever. Reality: fraud and customer behavior change, creating concept drift.
Myth: One unusual location or device proves fraud. Reality: individual signals require context.
Myth: Generative AI and fraud scoring are the same technology. Reality: they are different AI use cases.
Myth: AI eliminates the need for payment security. Reality: it complements tokenization, 3DS, PCI DSS, account security, and secure checkout architecture.
Conclusion
AI and machine learning have transformed payment fraud detection because they can evaluate far more context than a traditional rule engine while making decisions fast enough for modern digital commerce.
The strongest systems learn what legitimate activity looks like, identify departures from that behavior, compare new transactions with known fraud, and use network intelligence to detect patterns that no individual merchant can see alone.
But AI is not magic.
A risk score is an estimate, not proof. Models can drift, data can be mislabeled, legitimate customers can look unusual, and criminals can adapt.
That is why effective fraud prevention combines models with rules, EMV 3-D Secure, tokenization, account protection, secure payment pages, human investigation, and continuous feedback.
The future of payment security is therefore not AI replacing every other control. It is AI making layered security faster, more contextual, and better able to distinguish fraud from genuine customer behavior.