

What Is a Man-in-the-Middle Attack?
Complete Guide to Understanding, Detecting, and Preventing MitM Attacks
Definition
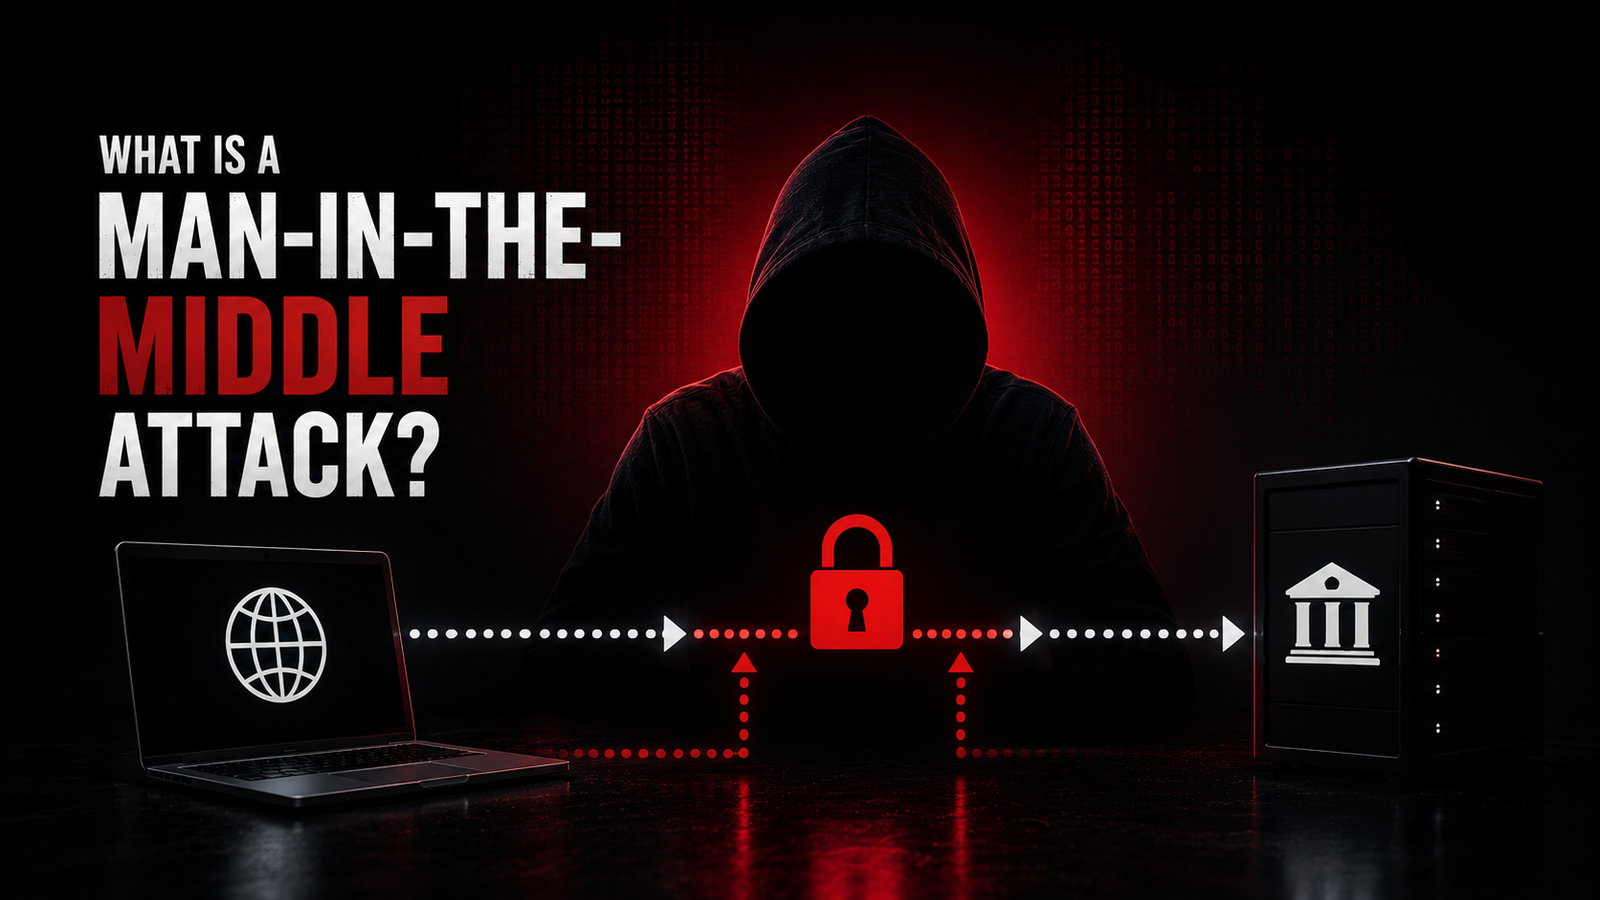
A Man-in-the-Middle (MitM) attack occurs when an attacker secretly intercepts, monitors, and potentially alters communication between two parties who believe they are directly communicating with each other.
The Analogy:
Imagine sending a sealed letter to your bank. A MitM attack is like someone secretly opening your mail, reading it, potentially changing the contents, resealing it, and forwarding it to your bank—all without either you or the bank knowing someone intercepted the communication.
In Digital Terms:
The "man" (attacker) positions themselves between your device (computer, phone) and the legitimate service (bank website, email server), intercepting data flowing in both directions.
How MitM Attacks Work
The Attack Chain
LEGITIMATE COMMUNICATION:You ←————————→ Bank Website
↑
↓
Data flows directly
MITM ATTACK:
You ←——→ Attacker ←——→ Bank Website
↑
↓
Attacker intercepts, reads, modifies all data
Step-by-Step Process:
- Interception: Attacker positions themselves on the communication path
- Impersonation: Attacker presents themselves as the legitimate recipient to both parties
- Relay: Attacker forwards communications while monitoring content
- Modification (Optional): Attacker alters data before forwarding
- Extraction: Attacker harvests credentials, session tokens, or sensitive data
Types of Man-in-the-Middle Attacks
1. Wi-Fi Eavesdropping (Evil Twin)
How It Works:

- Attacker creates a fake Wi-Fi network with a name similar to legitimate networks (e.g., "Starbucks_Free" vs "Starbucks_Free_WiFi")
- Victims connect to the rogue network
- Attacker monitors all traffic passing through their fake hotspot
- Can inject malicious content or redirect to phishing sites
Real-World Scenario:
You're at a coffee shop and connect to "Airport_Free_WiFi" (attacker's network). You log into your bank. The attacker captures your login credentials and session cookies.
Red Flags:
- Networks with slight misspellings
- "Free" networks in paid locations
- Networks with stronger signals than expected
- Captive portals asking for excessive information
2. ARP Spoofing (ARP Poisoning)
How It Works:
- ARP (Address Resolution Protocol) maps IP addresses to MAC addresses on local networks
- Attacker sends fake ARP messages to network devices
- Associates attacker's MAC address with legitimate IP addresses
- All network traffic intended for the legitimate device now flows through attacker
Technical Details:
Normal ARP:Device A (192.168.1.10) → Router (192.168.1.1)
ARP Spoofing:
Device A → Attacker → Router
Attacker claims to be both Device A and Router
Targets:
- Corporate networks
- Public Wi-Fi
- Shared office spaces
- Hotel networks
3. DNS Spoofing (DNS Cache Poisoning)
How It Works:

- DNS translates domain names (bank.com) to IP addresses
- Attacker corrupts DNS cache to point legitimate domains to malicious IP addresses
- Victims type correct URL but reach attacker's fake website
Attack Methods:
- Compromising DNS servers
- Local DNS cache poisoning
- Router DNS hijacking
- ISP-level DNS manipulation
Example:
Legitimate: bank.com → 203.0.113.1 (real bank server)Poisoned: bank.com → 198.51.100.5 (attacker's fake site)
Result: User sees correct URL in address bar but is on attacker's phishing site.
4. SSL/TLS Stripping (HTTPS Downgrading)
How It Works:
- Attacker intercepts HTTPS connection requests
- Forces connection to downgrade to unencrypted HTTP
- User sees "http://" instead of "https://" (often subtle or hidden)
- All data transmitted in plaintext, readable by attacker
Tools Used:
- SSLstrip (popular MitM tool)
- Bettercap
- Ettercap
- Burp Suite (for testing)
Why It Works:
- Many sites still accept HTTP connections
- Users don't notice missing padlock icon
- Some browsers auto-correct http to https, but attackers use techniques to prevent this
5. IP Spoofing
How It Works:
- Attacker forges source IP address in packet headers
- Makes packets appear to come from trusted source
- Used in combination with other MitM techniques
- Enables session hijacking and bypassing IP-based authentication
6. Email Hijacking (Man-in-the-Mailbox)
How It Works:
- Attacker gains access to email server or individual email accounts
- Monitors communications between parties
- Intercepts sensitive documents (invoices, wire transfer instructions)
- Modifies bank account numbers in payment requests
- Forwards altered emails to intended recipients
Business Email Compromise (BEC):
- $2.9 billion in losses annually
- Attacker intercepts vendor payment emails
- Changes wire transfer instructions
- Companies send payments to attacker-controlled accounts
7. Session Hijacking
How It Works:
- Attacker steals session cookies/tokens after legitimate authentication
- Uses stolen session to impersonate user
- Bypasses username/password requirements
- Can persist even after password change
Cookie Theft Methods:
- Packet sniffing on unsecured networks
- XSS (Cross-Site Scripting) attacks
- Malware reading browser cookie stores
- Session fixation attacks
Real-World Attack Scenarios
Scenario 1: Banking Session Theft
The Setup:
- Victim connects to hotel Wi-Fi (compromised by attacker)
- Victim logs into online banking (legitimate HTTPS connection)
- Attacker performs SSL stripping attack
- Connection downgrades to HTTP without victim noticing
- Attacker captures login credentials and session cookie
- Attacker uses stolen session to transfer funds
- Victim sees "session expired" message, logs in again
- Attacker now has second session, continues draining account
Financial Impact: Complete account takeover, unauthorized wire transfers
Scenario 2: Invoice Interception (BEC)
The Setup:
- Accounting firm emails client invoice with wire instructions
- Attacker has compromised email server
- Attacker intercepts email, modifies bank account number
- Client receives email (appears legitimate, from correct address)
- Client sends $50,000 payment to attacker's account
- Attacker forwards original email to cover tracks
- Real vendor never receives payment
Financial Impact: Direct theft of business funds, difficult to recover
Scenario 3: Cryptocurrency Exchange Theft
The Setup:
- Trader accesses crypto exchange via public Wi-Fi
- Attacker performs ARP spoofing on local network
- Attacker intercepts API keys transmitted by trading app
- Attacker uses API keys to access exchange account
- Attacker drains cryptocurrency to external wallets
- Trader sees unauthorized withdrawals
Financial Impact: Irreversible cryptocurrency theft
How to Detect MitM Attacks
Warning Signs
| Indicator | What It Means | Check Method |
| Certificate warnings | Invalid SSL/TLS certificate | Browser shows "Not Secure" warning |
| URL anomalies | HTTP instead of HTTPS | Check address bar for padlock icon |
| Slow connections | Traffic routed through attacker | Compare speed to normal |
| Unexpected logouts | Session stolen by attacker | Monitor login notifications |
| Changed website appearance | DNS spoofing to fake site | Compare to known legitimate site |
| Multiple 2FA requests | Attacker attempting access | Check login location notifications |
| Network anomalies | ARP spoofing active | Check ARP tables (technical) |
Technical Detection Methods
Check SSL Certificates:
- Click padlock icon in browser
- View certificate details
- Verify issuer is legitimate (DigiCert, Let's Encrypt, etc.)
- Check expiration date
- Verify domain matches exactly
Monitor Network Traffic:
bash
# Check ARP table for duplicates (Linux/Mac)arp -a
# Look for multiple IPs with same MAC address# (Indicates ARP spoofing)
Verify DNS Resolution:
bash
# Check DNS resolution (Linux/Mac/Windows)nslookup bank.com# Compare to known legitimate IP# If different, possible DNS poisoning
Prevention Strategies
1. Network Security
Avoid Public Wi-Fi for Sensitive Activities:
- Never access banking on public Wi-Fi without VPN
- Use mobile hotspot instead of public networks
- If public Wi-Fi necessary, always use VPN
Use a VPN (Virtual Private Network):
- Encrypts all traffic between device and VPN server
- Prevents local network attackers from intercepting data
- Recommended providers: ProtonVPN, Mullvad, NordVPN
Verify Network Legitimacy:
- Ask staff for official network name
- Check for HTTPS on captive portals
- Be suspicious of networks requiring excessive personal info
2. HTTPS and Certificate Verification
Always Verify HTTPS:
- Look for padlock icon in address bar
- Verify URL spells correctly (no homograph attacks)
- Never enter credentials on HTTP sites
HSTS (HTTP Strict Transport Security):
- Browser security feature
- Forces HTTPS connections to sites
- Prevents SSL stripping attacks
- Enable in browser settings
Certificate Pinning:
- Mobile apps validate specific certificates
- Prevents accepting fraudulent certificates
- Used by banking apps
3. DNS Security
Use Secure DNS:
- DNS over HTTPS (DoH): Encrypts DNS queries
- DNS over TLS (DoT): Alternative encryption method
- DNSSEC: Validates DNS responses
Recommended DNS Providers:
- Cloudflare (1.1.1.1)
- Quad9 (9.9.9.9)
- Google DNS (8.8.8.8)
Browser Configuration:
Chrome: Settings → Privacy → Security → Use secure DNSFirefox: Settings → Network → Enable DNS over HTTPS
4. Endpoint Security
Keep Software Updated:
- Browser updates include security patches
- OS updates fix network stack vulnerabilities
- App updates patch MitM vulnerabilities
Use Security Software:
- Antivirus with network monitoring
- Anti-malware with real-time protection
- Browser extensions: HTTPS Everywhere
Browser Extensions:
- HTTPS Everywhere: Forces HTTPS connections
- uBlock Origin: Blocks malicious scripts
- Certificate Patrol: Alerts on certificate changes
5. Authentication Security
Multi-Factor Authentication (MFA):

- Even if credentials stolen, 2FA prevents access
- Use authenticator apps, not SMS (vulnerable to SIM swapping)
- Hardware security keys most resistant to MitM
Session Management:
- Log out completely when finished
- Clear cookies regularly
- Use private browsing for sensitive sites
- Monitor active sessions in account settings
Out-of-Band Verification:
- Confirm wire transfers via phone call
- Verify payment instructions through secondary channel
- Don't rely solely on email for financial transactions
6. Corporate/Enterprise Protection
Network Segmentation:
- Isolate critical systems from general network
- Separate banking computers from general use
- Use VLANs to segment traffic
ARP Spoofing Detection:
- Tools: Arpwatch, XArp, Cain & Abel
- Monitor for duplicate MAC addresses
- Alert on ARP table changes
Encrypted VPN Tunnels:
- Force all traffic through corporate VPN
- Prevents local network attacks
- Centralized traffic monitoring
MitM Attack Tools (For Security Testing)
Legitimate Security Tools:
- Wireshark: Network protocol analyzer
- Burp Suite: Web vulnerability scanner
- OWASP ZAP: Web application security testing
- Ettercap: Network security testing
- Bettercap: Network attack framework
Important: These tools should only be used on networks you own or have explicit permission to test.
Legal and Ethical Considerations
MitM attacks are illegal when:
- Conducted without authorization
- Used to steal credentials or data
- Performed on networks you don't own
- Used for financial fraud or identity theft
Legitimate Uses:
- Security research with permission
- Network troubleshooting
- Penetration testing (authorized)
- Educational demonstrations on owned networks
Summary
Key Takeaways
MitM attacks silently intercept communications between you and legitimate services
Public Wi-Fi is the highest risk - always use VPN or avoid sensitive activities
HTTPS is essential but not foolproof - verify certificates and watch for SSL stripping
DNS security matters - use secure DNS and verify you're reaching legitimate sites
MFA provides strong protection even if credentials are intercepted
Verify financial instructions through out-of-band channels (phone calls)
Monitor for warning signs - certificate errors, slow connections, unexpected logouts
Defense Checklist
- Use VPN on public Wi-Fi
- Verify HTTPS on all sensitive sites
- Enable secure DNS (DoH)
- Use MFA on all accounts
- Keep browsers and OS updated
- Verify SSL certificates
- Log out of accounts when finished
- Confirm financial instructions by phone
- Monitor account for unauthorized access
- Use security software with network protection
This guide is for educational and fraud awareness purposes. Understanding MitM attacks helps individuals and organizations implement appropriate security controls to protect sensitive communications and financial transactions.
Remember: The most effective defense against MitM attacks is layered security—combining encrypted connections, verified certificates, secure DNS, multi-factor authentication, and vigilant monitoring of network activity and account access.