What to Do If Someone Has Your Credit Card Information: Immediate Steps to Take
If you discover that someone may have your credit card number, expiration date, security code or other payment information, acting quickly can re...

Independent fraud-awareness editors.
If you discover that someone may have your credit card number, expiration date, security code or other payment information, acting quickly can re...
Small businesses face payment-fraud risks in two very different environments: card-present transactions, where the customer and payment card are...
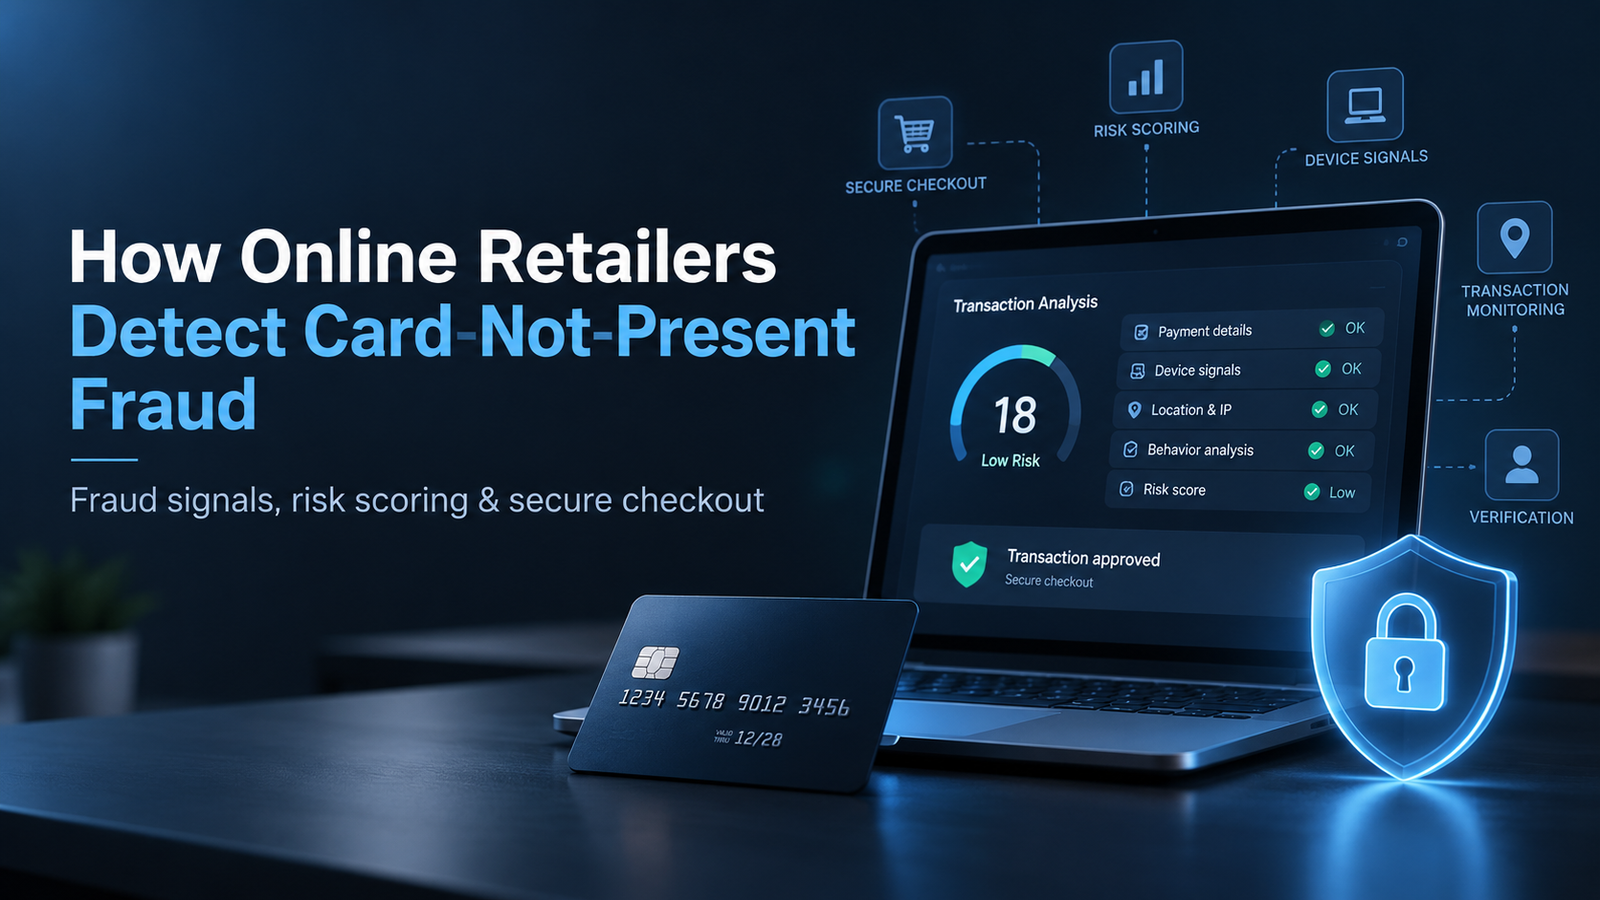
Online retailers cannot physically inspect a customer's payment card during an ecommerce purchase. That makes card-not-present (CNP) fraud detect...
Online businesses can reduce card-not-present (CNP) fraud by using layered security rather than relying on a single check. Effective controls inc...
Card-not-present fraud, commonly shortened to CNP fraud, is payment fraud that occurs when a purchase is made without the physical payment card b...

VBV stands for Verified by Visa, the former name of Visa’s online cardholder-authentication program. Today the service is known as Visa Secure an...
PAN stands for Primary Account Number. It is the unique payment-card number associated with a credit, debit or prepaid card account and is one of...

Card-not-present (CNP) fraud occurs in payment environments where a physical card is not presented to the merchant, including ecommerce, in-app p...
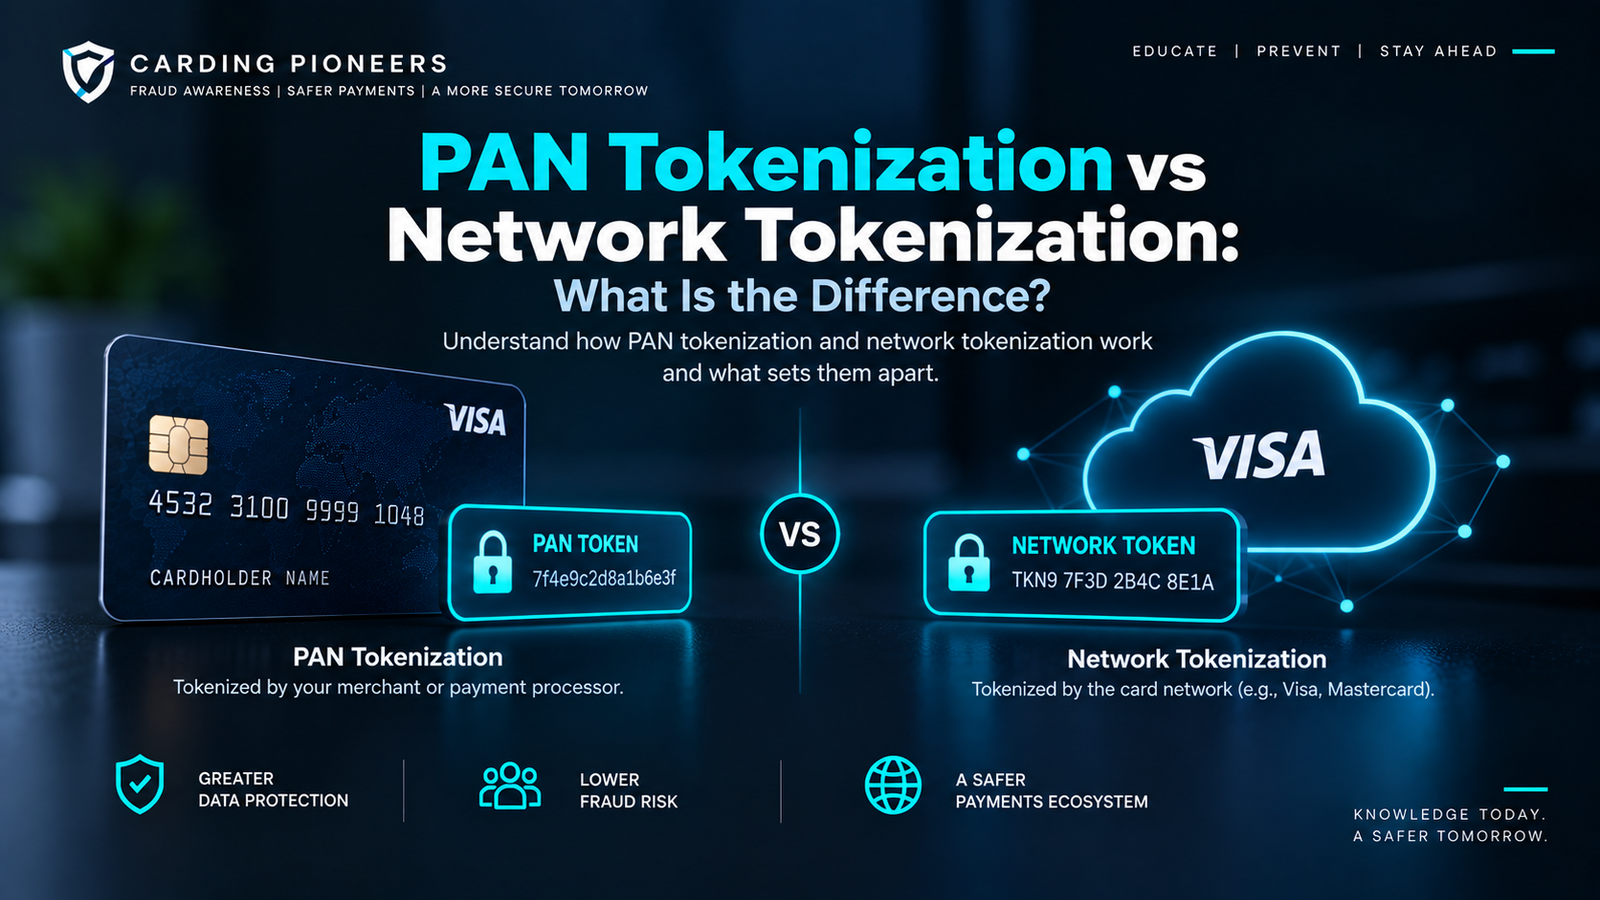
PAN tokenization and network tokenization both reduce exposure of a card's Primary Account Number (PAN), but they do not work in exactly the same...

“Non-VBV” is an informal term used to describe an online card payment that does not show the older Verified by Visa authentication step. It is no...

Credit card information can be stolen even when the physical card never leaves your wallet. This guide explains the most common ways card data is...
Phishing, smishing and vishing are related social-engineering scams delivered through different channels. This guide explains how they differ, wh...